Enterprise Risk
Enterprise Risk — One Index Across Every Domain
Observeri Enterprise Risk lets the organisation define the taxonomy, appetite, matrix, limits, enterprise KRIs, and workflows. Every domain augments one global risk index. Each threshold carries the response designed for that breach, and a critical risk opens a real-time war room.
Index
All domains
Board
Ready packs
Live
War rooms
Enterprise risk management for enterprises, SMEs, and startups
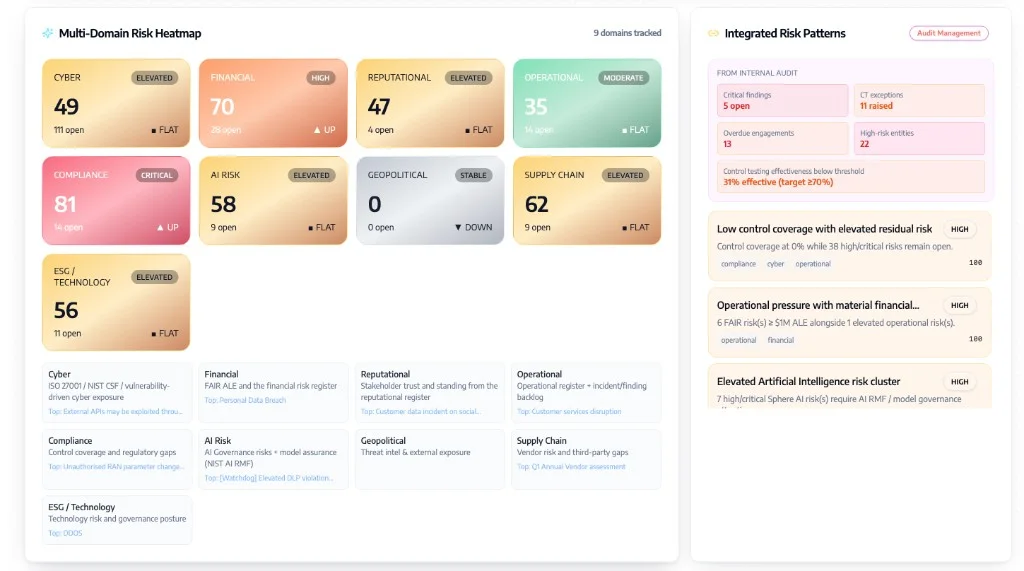
Cyber, financial, reputational, operational, compliance, AI, geopolitical, supply chain, and ESG and technology keep their own position. Board-ready packs take the index, the heatmap, and the patterns that cross those domains.
Why it matters
The board sees nine conversations and no index
Domains never meet
Cyber, financial, operational, compliance, and the rest each report a score. Nothing adds them into one enterprise position.
Taxonomy is a slide
Appetite, the matrix, and limits are redefined in every committee. A breach has no designed response.
A critical risk has no room
When a risk turns critical, people open email. There is no live place to watch that risk until it moves.
The board pack is assembled late
Integrated patterns across audit, cyber, and finance are written the night before the meeting.
The Observeri approach
Every domain augments one global risk index
One index from every domain
Cyber, financial, reputational, operational, compliance, AI, geopolitical, supply chain, and ESG and technology each contribute. Together they are the global risk index.
The enterprise sets the rules
Taxonomy, risk matrix, appetite, limits, enterprise KRIs, and workflows are defined once and applied to every domain.
A breach already has a design
Each threshold carries the response designed for that breach: the workflow, the owner, and whether a war room opens.
Critical risks are watched live
A war room stays on a critical risk in real time. The same view feeds the board-ready pack.
How it works
From the taxonomy to a live room on a critical risk
Define taxonomy, appetite, matrix, limits, and KRIs. Every domain augments the global risk index. A breach follows the response designed for it, and a critical risk opens a war room.
Step 1
Define the taxonomy
The enterprise language for risk
Set the risk taxonomy the whole organisation uses, so cyber, financial, operational, and the other domains are classified the same way.
Includes
Platform features
What the enterprise defines once
Global risk index
Every risk domain augments one index, with direction and open risks visible by domain.
Risk taxonomy
The classification the enterprise defines, shared by cyber, financial, operational, and the other domains.
Thresholds and breach design
Each threshold carries the response designed for that breach, including who acts and which workflow starts.
Enterprise KRIs
Indicators defined for the enterprise and mapped onto the taxonomy and the index.
Risk appetite
Appetite set by the enterprise and applied when a domain or a risk is placed.
Workflows
The paths the enterprise designs for assessment, breach, escalation, and response.
Risk matrix and limits
The matrix and the limits the enterprise sets, used to place and test each risk.
Board-ready packs
The index, the domain heatmap, and cross-domain patterns assembled for the board.
Risk response
The response chosen for the risk, kept on the record from the breach through to closure.
Real-time war rooms
A live room on a critical risk, so that risk is monitored until it is no longer critical.
Outcomes
One index, a designed breach, a room when it is critical
The board sees one index
Domains still have their own position. The global risk index is what they add up to.
A breach is not improvised
The threshold already holds the workflow, the owner, and the response designed for that breach.
A critical risk has a room
The war room stays on that risk in real time, and the same picture can go into the board pack.
Platform capabilities
The index and the rules underneath it
Cyber, financial, reputational, operational, compliance, AI, geopolitical, supply chain, and ESG and technology each keep their own position. The global risk index is what those domains augment.
- Global risk index augmented by every risk domain
- Enterprise-defined risk taxonomy
- Risk thresholds with the response designed for each breach
- Enterprise KRIs mapped to the taxonomy and the index
- Risk appetite, risk matrix, and risk limits set by the enterprise
- Workflows for assessment, breach, escalation, and response
- Board-ready packs from the index, the heatmap, and cross-domain patterns
- Real-time war rooms to monitor a critical risk
Enterprise scope
1
Global risk index
9
Domains on the heatmap
Live
War rooms
Board
Ready packs
Give the board one index and a room for what is critical
Roll every risk domain into a global risk index, design the response on each breach, and open a real-time war room when a risk is critical.
Frequently asked questions
What is the global risk index?
The global risk index is the combined position of every risk domain. Each domain keeps its own score and direction, and those domains augment the single enterprise index.
What can the enterprise define?
The enterprise defines the risk taxonomy, risk appetite, risk matrix, risk limits, enterprise KRIs, and workflows. Each threshold also holds the response designed for that breach.
What is a war room?
A war room is a real-time view opened on a critical risk. It stays on that risk, with the domains, indicators, and actions moving it, until the risk is no longer critical.
Related products
Cyber Risk Management
Live risk scoring, control mapping, FAIR quantification, and smart remediation.
Operational Risk
RCSA, live KRIs, loss events, and operational capital under Pillar 1 and Pillar 2, with back-testing.
Financial Risk
Capital, market, and liquidity risks monitored against organisation-defined limits, with regulatory capital impact.
Observeri
AI agent
Welcome to Observeri - My Name is Misha, How may i help you today!
Your privacy choices
We use essential storage to remember your choices. With your permission, we also use analytics to understand website usage and marketing technologies to measure advertising, plus YouTube to show product videos. Optional tracking stays off until you choose. Read our Privacy Policy.