Compliance Management
From regulation to evidence—compliance that runs itself
Observeri Compliance Management lets teams maintain regulations and standards, auto-build compliance registers from uploaded documentation, run AI self-assessments with confidence-scored results, track regulatory submissions, manage incidents and breaches, and compare policies against requirements with AI remediation guidance.
AI
Register generation
Live
Compliance scores
SLA
Submission tracking
Why it matters
Compliance programmes drown in manual mapping and stale registers
Registers built by hand, once a year
Teams manually transpose regulation text into spreadsheets—missing implementation guidance, expected evidence, and updates when standards change.
Assessments are point-in-time snapshots
Self-assessments happen before audits but rarely between cycles—so control drift and document gaps accumulate unnoticed.
Regulatory submissions slip through cracks
Filings and notifications to regulators lack centralized SLA tracking, ownership, and escalation when deadlines approach.
Policies diverge from requirements
Procedural documents age without systematic comparison against current regulations—creating audit findings and regulatory exposure.
What it is
AI-powered compliance operations from register to remediation
Compliance Management is Observeri's end-to-end module for regulatory adherence. Upload a regulation or standard and AI builds your compliance register with implementation guidance and expected evidence. Horizon scanning self-assessments score control and document compliance with confidence levels—while submission tracking, incident management, and policy comparison keep the programme current.
Regulations & Standards Library
Maintain a living library of compliance regulations and standards—ISO 27001, SOC 2, NIST, GDPR, PDPL, HIPAA, PCI DSS, SWIFT, DORA, and regional frameworks—with version history and applicability scope.
AI Compliance Register
Upload regulation or standard documentation and AI automatically generates a structured compliance register—requirements, implementation guidance, expected evidence, and control mappings ready for assessment.
AI Self-Assessment & Horizon Scanning
Automated horizon scanning across controls and documents produces compliance scores with confidence levels—showing how existing controls measure against each regulatory requirement in real time.
Regulatory Submissions Tracking
Track regulatory submissions and filings to authorities with defined SLAs, assigned ownership, status workflows, and automated alerts when submission deadlines approach or breach.
Compliance Incidents & Breaches
Maintain a register of compliance incidents and breaches—from intake and classification through investigation, regulatory notification, and verified closure with evidence.
AI Policy Comparison & Guidance
Compare company policy and procedural documents against regulations and standards. AI identifies gaps, explains misalignment, and provides actionable remediation guidance to close deficiencies.
Auto-build registers
Score with confidence
Close gaps with AI
How it works
Maintain. Register. Assess. Track. Remediate.
A continuous compliance loop—from AI register generation and horizon scanning through submission tracking, incident management, and policy gap remediation.
Step 1
Maintain
Curate your regulations and standards library
Build and maintain the regulatory frameworks your organization must adhere to—selecting applicable standards, tracking versions, and defining scope by business unit, geography, or entity.
Activities
Platform features
Six sub-modules. One compliance programme.
Living regulations library
Centralize every regulation and standard your organization follows—with version control, applicability tags, and links to generated registers.
Upload-to-register AI
Drop in a regulation PDF or standard document and AI extracts obligations, implementation steps, and expected evidence into an audit-ready register.
Confidence-scored assessments
Horizon scanning evaluates controls and documents against each requirement—outputting compliance scores with AI confidence levels teams can defend to auditors.
Submission SLA management
Never miss a regulatory filing—track submissions with owners, deadlines, SLA aging alerts, and status from draft through accepted.
Incident & breach management
Manage compliance incidents and breaches end-to-end—with severity classification, regulatory notification tracking, and closure evidence.
AI policy gap analysis
Side-by-side comparison of policies and procedures against regulatory text—with AI-generated remediation guidance for every identified gap.
Benefits for your organization
Run compliance as a continuous programme—not a pre-audit scramble
Registers in hours, not months
AI register generation from uploaded documentation eliminates manual transcription—giving teams implementation guidance and expected evidence from day one.
Continuous compliance visibility
Horizon scanning and confidence-scored self-assessments replace annual checkbox exercises—surfacing control drift and document gaps between formal audits.
Regulatory obligations never missed
Submission tracking with SLAs and ownership ensures filings and notifications reach regulators on time—with full audit trails of who submitted what and when.
Policies aligned to current regulation
AI policy comparison keeps procedural documents synchronized with evolving standards—closing the gap between what is written and what regulators expect.
Audit-ready evidence on demand
Compliance registers link requirements to controls, documents, and evidence—so auditors receive structured proof instead of last-minute document hunts.
Faster breach and incident response
Centralized compliance incident and breach management with regulatory notification workflows compresses response time when obligations are triggered.
Measurable programme maturity
Compliance scores with confidence levels trend over time—giving boards and regulators quantified proof of programme improvement, not narrative alone.
Platform capabilities
Enterprise compliance management, end to end
- Regulations and standards library with multi-framework support and version tracking
- AI compliance register generation from uploaded regulation and standard documentation
- Implementation guidance and expected evidence auto-mapped to each requirement
- Automated self-assessment through AI horizon scanning on controls and documents
- Compliance score and confidence level per requirement against existing controls
- Regulatory submission tracking with SLA deadlines, ownership, and aging alerts
- Compliance incidents and breaches register with investigation and notification workflows
- AI comparison of company policies and procedures against regulations and standards
- AI-generated remediation guidance for policy and control gaps
- Gap registers with prioritization and linkage to Focused Remediation programmes
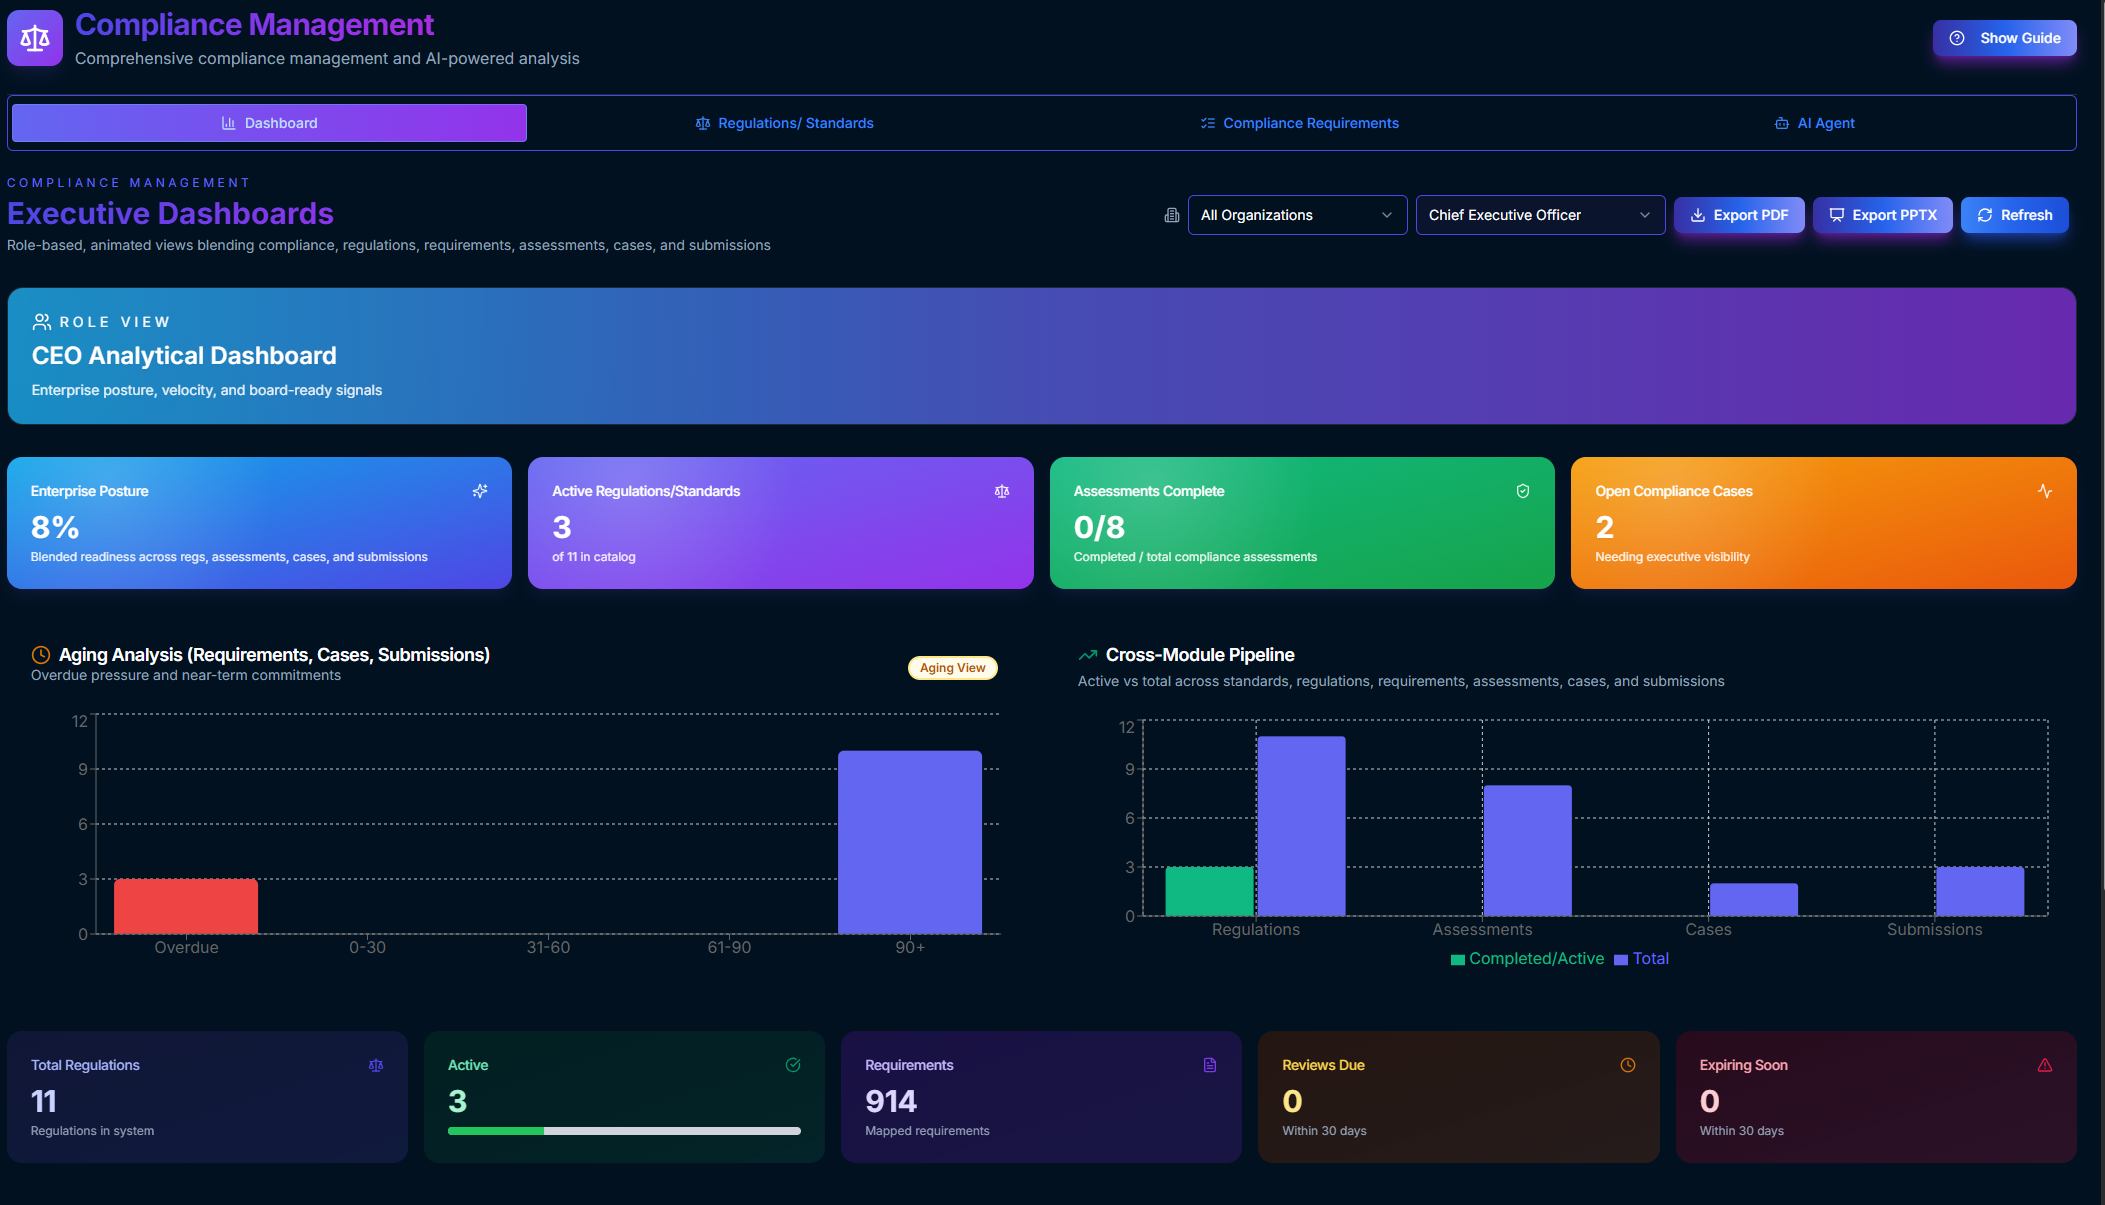
- Scheduled assessment cadence with trend tracking and executive dashboards
- Integration with Security Governance, Exposure Management, and AI Risk Operations Center
Quantified outcomes
200+
Supported frameworks
AI
Register & assessment
100%
SLA-tracked submissions
24/7
Horizon scanning
Connected to Observeri GRC
Compliance Management integrates with Security Governance, Data Privacy & Protection, and Exposure Management—so registers, assessments, and remediation stay connected across the platform.
From regulation upload to confidence-scored compliance
Build AI-powered compliance registers, run horizon scanning self-assessments, track regulatory submissions, manage incidents, and close policy gaps—all in one module.