Security Governance
Govern security with metrics, policies, budgets, and controlled change
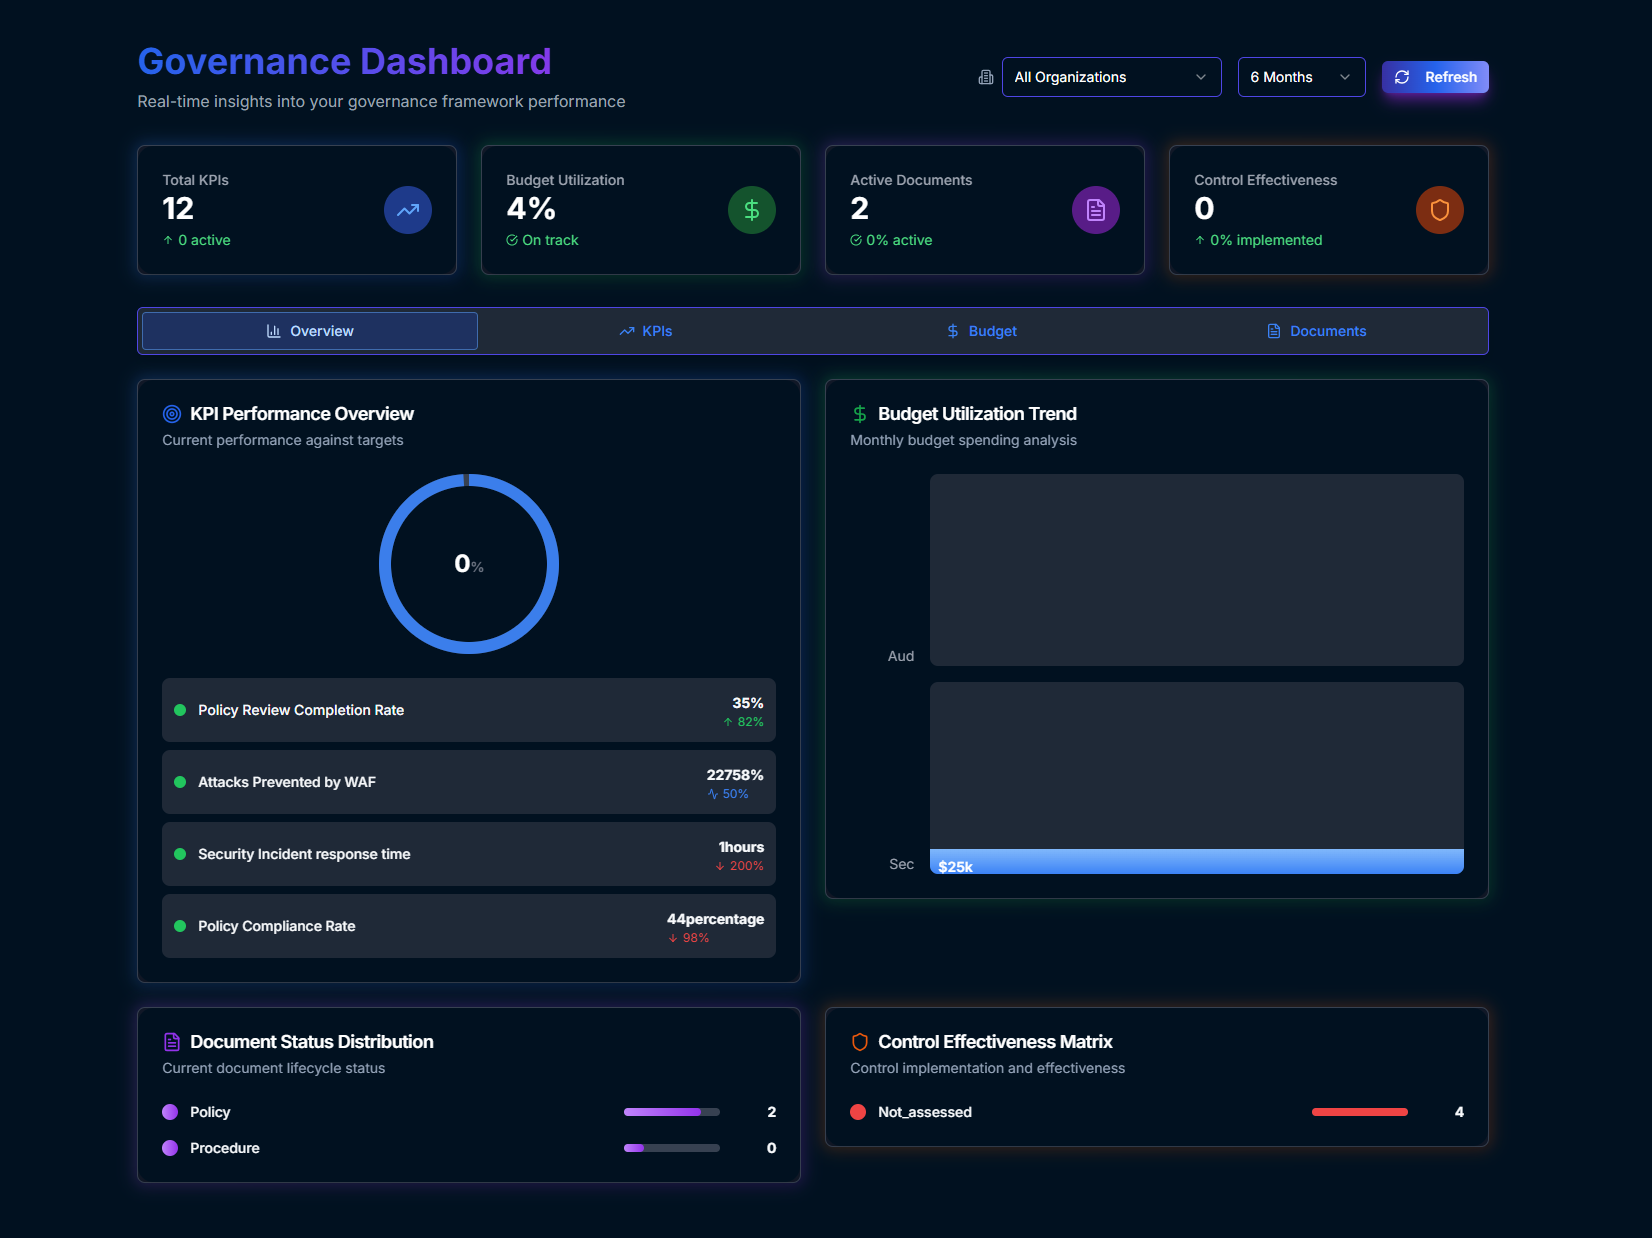
Observeri Security Governance unifies KRI/KPI monitoring, policy management, AI budgeting, change management for security tools and processes, and dedicated project management—giving boards and CISOs one workspace to steer the security programme with evidence.
Live
KRI/KPI dashboards
AI
Budget optimization
100%
Governed change trail
Why it matters
Security governance still runs on decks, not data
KRIs and KPIs live in slide decks
Governance metrics are rebuilt manually each quarter from scattered sources—so boards see lagging indicators, not live programme health.
Policies drift from reality
Policy libraries age without systematic review, gap analysis against frameworks is manual, and teams cannot prove alignment when auditors ask.
Budgets disconnected from risk
Security spend is allocated by history and politics—not by quantified exposure, expected risk reduction, or AI-informed investment scenarios.
Tool and process changes go untracked
New security tools, configuration shifts, and process updates happen without structured change management—creating governance gaps and audit findings.
What it is
The strategic control plane for your security programme
Security Governance is Observeri's executive and operational layer for steering cyber security. Five integrated sub-modules—KRI/KPI monitoring, policy management, AI budgeting, change management, and project management—connect governance metrics to the tools, spend, and programmes that actually reduce risk.
KRI / KPI Monitoring
Define governance key risk and performance indicators, track them on live dashboards, and alert leadership when metrics breach thresholds—replacing quarterly slide rebuilds with continuous programme visibility.
Policy Management
Generate framework-aligned policies with AI, compare documents against regulatory requirements, manage version control and approvals, and produce gap reports auditors can trust.
AI Budgeting
Plan security budgets with AI-informed scenarios that tie spend to quantified risk reduction—comparing investment options by expected exposure collapse, not spreadsheet guesswork.
Change Management
Govern changes to security tools, configurations, and operational processes with structured intake, impact assessment, approval workflows, and a complete audit trail.
Project Management
Run dedicated security governance and improvement projects with milestones, ownership, dependencies, and linkage to KRI/KPI outcomes—so initiatives deliver measurable programme progress.
Measure what matters
Govern with evidence
Invest with intelligence
How it works
Define. Plan. Govern. Monitor. Improve.
A continuous governance cycle connecting metrics, policies, budgets, controlled change, and project delivery—so security leadership steers with live data.
Step 1
Define
Set KRIs, KPIs, and policy baselines
Establish the governance metrics that matter to your board and regulators, upload or generate policies aligned to your frameworks, and configure the indicators that will measure programme health going forward.
Activities
Platform features
Five sub-modules. One governance workspace.
Live KRI/KPI dashboards
Board and CISO dashboards track governance metrics continuously—incident rates, control effectiveness, remediation velocity, compliance scores, and custom KRIs you define.
AI-powered policy lifecycle
Generate, compare, and gap-analyze policies against ISO 27001, NIST, SOC 2, and other frameworks—with version control and approval workflows built in.
Risk-informed AI budgeting
Model security spend scenarios with AI that connects investment options to expected risk reduction—helping CFOs and CISOs justify budgets with quantified outcomes.
Security change management
Structured workflows for changes to security tools, cloud configurations, access models, and operational processes—with impact assessment and full audit trails.
Governance project management
Dedicated project workspaces for security initiatives—with tasks, milestones, dependencies, and linkage to the KRI/KPI metrics they are designed to improve.
Unified governance reporting
Combine metrics, policy status, budget utilization, change records, and project progress into executive reports—replacing fragmented governance packs.
Benefits for your organization
Governance that boards, auditors, and CISOs can all trust
Board-ready visibility without manual rebuilds
KRIs and KPIs update from live platform data—so governance reporting reflects current programme health instead of stale quarterly snapshots assembled in PowerPoint.
Policies that stay aligned to regulation
AI comparison and scheduled review cycles keep policy libraries current—closing the gap between what is documented and what auditors and regulators expect.
Security budgets tied to risk outcomes
AI budgeting connects spend decisions to quantified exposure reduction—so investment conversations shift from cost centers to measurable risk management.
Controlled change with complete audit trails
Every change to security tools and processes is documented, assessed, approved, and traceable—reducing governance gaps and strengthening audit defensibility.
Governance that runs every day, not once a quarter
Continuous KRI/KPI monitoring, live policy status, and active project tracking mean governance is operational—not a periodic reporting exercise disconnected from SecOps reality.
Faster, evidence-based board conversations
CISOs walk into board meetings with current metrics, budget scenarios, and project progress—grounding strategic decisions in data instead of narrative alone.
Programme improvements with accountable delivery
Dedicated project management linked to governance metrics ensures security initiatives have owners, milestones, and measurable outcomes—not open-ended task lists.
Platform capabilities
Enterprise security governance, end to end
- KRI and KPI definition with configurable thresholds, targets, and breach alerting
- Live governance dashboards fed by operational data across the Observeri platform
- AI-generated policies aligned to selected compliance and security frameworks
- Document upload with automated regulatory gap analysis and side-by-side comparison
- Policy version control, approval workflows, and audit-ready change history
- AI budgeting with spend-vs-risk scenarios and investment optimization recommendations
- Change management workflows for security tools, configurations, and processes
- Impact assessment and multi-stage approval routing for governed changes
- Dedicated security project management with milestones, tasks, and dependencies
- Project-to-KRI/KPI linkage for measurable governance improvement tracking
- Executive governance reporting combining metrics, policies, budgets, and projects
Quantified outcomes
80+
Governance dashboards
5
Integrated sub-modules
AI
Budget & policy intelligence
24/7
KRI/KPI monitoring
Connected to Observeri GRC
Security Governance feeds from and informs the AI Risk Operations Center, Compliance Management, and Executive Dashboards—so KRI/KPI metrics, budget decisions, and project outcomes reflect live risk and compliance posture across the platform.
Steer security with governance that runs on live data
Unify KRI/KPI monitoring, policy management, AI budgeting, change management, and project delivery in one governance workspace built for CISOs and boards.