Centralised Controls
Centralised Controls — Library, Testing, and Live Effectiveness
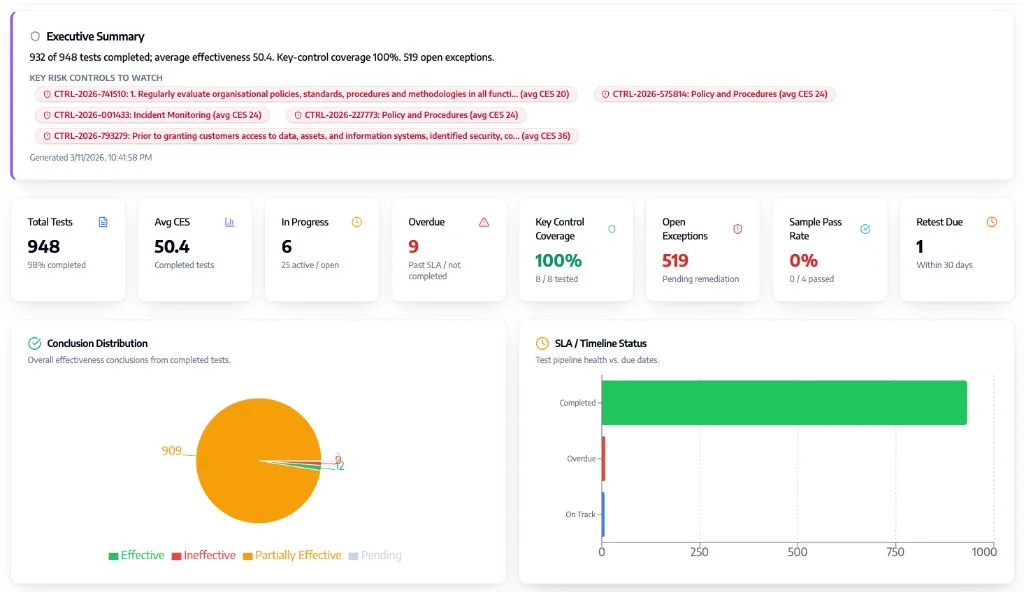
Observeri Centralised Controls Management holds a library of more than 3,000 controls. The organisation approves which controls apply, and users test those controls through a workflow, upload the evidence, and rate control effectiveness.
3,000+
Controls in the library
Test
Workflow and evidence
Live
Risk, compliance, incidents
Centralised controls management for enterprises, SMEs, and startups
When effectiveness is updated, every risk, compliance item, and incident the control maps to updates with it. The mapped records read the current rating instead of a copy from the last review.
Why it matters
A control is tested in one place and stale everywhere else
The library is a spreadsheet
Thousands of controls sit in copies. Nobody can say which ones the organisation has actually approved as applicable.
Testing leaves the workflow
A test is an email thread and a folder of files. The result never lands on the control that was supposed to be tested.
Evidence and the rating drift apart
Files are uploaded somewhere, and the effectiveness rating is typed somewhere else. The two are not the same record.
Mapped records keep the old score
Risk, compliance, and incidents still show the effectiveness from the last time someone remembered to copy it across.
The Observeri approach
One library, one test, and every mapped record moves with it
A library of 3,000+ controls
The controls library is the inventory. Each control is available to the organisation before anyone decides that it applies.
The organisation approves applicability
Applicability is a decision on the control: it applies, or it does not. Only an applicable control enters testing.
Test, evidence, and a rating
Users run the test through a workflow, upload the evidence, and rate the control effectiveness on that same control.
Mapped records update with the rating
When effectiveness changes, every risk, compliance item, and incident the control maps to updates with it.
How it works
From the library to every record the control maps to
Approve which controls apply, test them through a workflow with evidence, rate effectiveness, and let every mapped risk, compliance item, and incident update.
Step 1
Open the library
An inventory of 3,000+ controls
Start from the controls library. The inventory holds more than 3,000 controls, ready for the organisation to decide which ones apply.
Includes
Platform features
What centralised controls management keeps in one place
Controls library
An inventory of more than 3,000 controls, held in one library rather than in copied lists.
Applicability
The organisation approves whether each control applies before it enters testing.
Testing workflows
Users perform control testing through a workflow, with the test status on the control.
Evidence upload
Evidence is uploaded to the test, so the files and the control stay on one record.
Effectiveness rating
The tester rates control effectiveness, and that rating becomes the current score on the control.
Mapped risk
A changed effectiveness rating updates every risk the control maps to.
Mapped compliance
Compliance items mapped to the control take the new effectiveness with the same update.
Mapped incidents
Incidents mapped to the control update when the effectiveness rating changes.
Outcomes
One effectiveness rating, read everywhere it is mapped
Applicability is a decision
The library is large. The organisation approves which controls apply, and testing follows that decision.
The test carries its evidence
Workflow, uploaded evidence, and the effectiveness rating live on the control that was tested.
Mappings stay current
Risk, compliance, and incidents that use the control receive the new effectiveness when it is updated.
Platform capabilities
Library, test, and the records that depend on it
The organisation approves applicability from a library of more than 3,000 controls. A test uploads its evidence, the effectiveness rating is set, and every mapped risk, compliance item, and incident updates.
- Controls library with an inventory of more than 3,000 controls
- Applicability approved by the organisation before a control is tested
- Control testing performed through a workflow
- Evidence uploaded to the test
- Control effectiveness rated on the control
- Automatic update of every mapped risk, compliance item, and incident
- One current effectiveness score, read by every record the control maps to
Control scope
3,000+
Controls in the library
Apply
Organisation approved
Test
Workflow and evidence
Live
Mapped records update
Rate the control once, and every mapping moves with it
Keep a library of 3,000+ controls, approve applicability, test with evidence, and update mapped risk, compliance, and incidents when effectiveness changes.
Frequently asked questions
How does the organisation choose which controls apply?
The controls library is an inventory of more than 3,000 controls. The organisation approves applicability on each control, and only an applicable control enters the testing workflow.
How is a control tested and rated?
Users perform the test through a workflow, upload the evidence to that test, and rate the control effectiveness. The rating becomes the current score on the control.
What updates when control effectiveness changes?
Every risk, compliance item, and incident the control maps to updates automatically with the new effectiveness. Those records do not keep the previous rating.
Related products
Cyber Risk Management
Live risk scoring, control mapping, FAIR quantification, and smart remediation.
Compliance Management
Regulations library, AI compliance register, horizon scanning, submissions, incidents, and policy gap analysis.
Automated Compliance
On-prem agent for Windows and Linux, virtual connector for Azure, GCP, AWS, and Oracle Cloud, and a scheduled real-time risk view.
Observeri
AI agent
Welcome to Observeri - My Name is Misha, How may i help you today!
Your privacy choices
We use essential storage to remember your choices. With your permission, we also use analytics to understand website usage and marketing technologies to measure advertising, plus YouTube to show product videos. Optional tracking stays off until you choose. Read our Privacy Policy.