Data Loss Prevention
Data Loss Prevention — Approved Channels, Caught Shadow Mediums
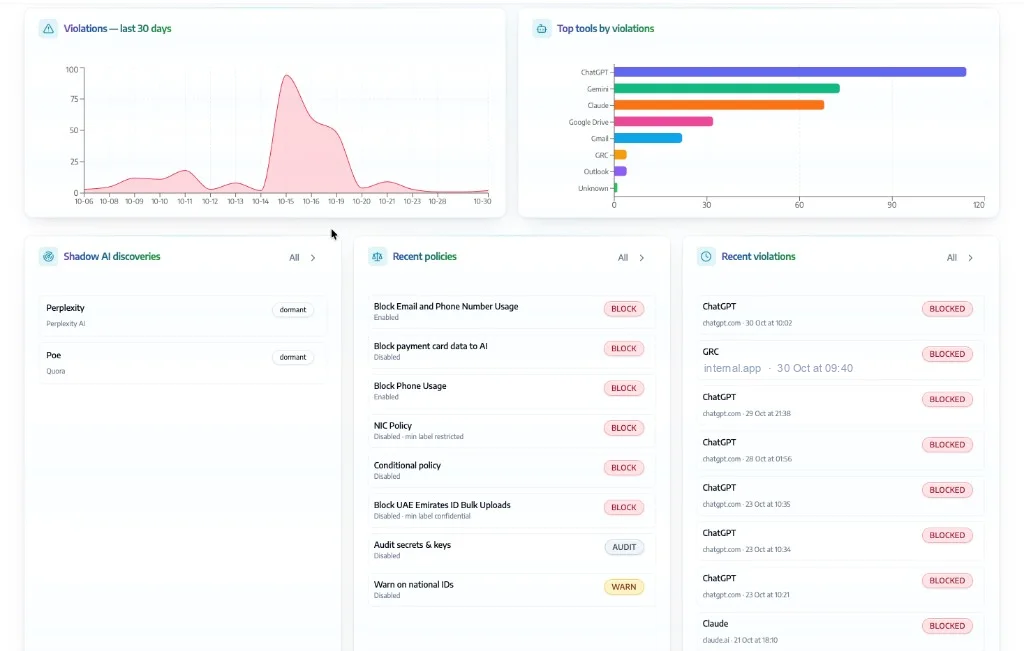
Observeri Data Loss Prevention starts with the channels the organisation approves: email service providers, cloud drive providers, and AI models. When someone uses a medium outside that list, the system catches the shadow use.
Approved
Email, drive, and AI
Shadow
Mediums caught
Incident
From a violation
Data loss prevention for enterprises, SMEs, and startups
Teams define the infotypes that matter and the policies that act on them. A policy can block, audit keywords, or audit files, and it sends the violation. From that violation, the team opens a risk incident.
Why it matters
Sensitive data leaves on a channel nobody approved
Approved tools are a list in a policy
Email, cloud drives, and AI models the organisation allows live in a document. People still send files from a personal mailbox or a drive that was never on the list.
Shadow mediums stay invisible
A dormant AI tool, an unknown drive, or a personal mail account moves data without appearing next to the approved providers.
Policies name the rule, not the data
A rule says not to share customer data. It does not say which infotypes to block, which keywords to audit, or which files to inspect.
A block ends at the alert
The violation is sent, then it sits in a feed. It never becomes a risk incident with an owner and a treatment.
The Observeri approach
Approve the channels, then catch everything else
Start with the approved providers
The organisation lists the email service providers, cloud drive providers, and AI models that are allowed. That list is the boundary.
Catch the shadow medium
When someone uses an email service, a cloud drive, or an AI model outside the approved list, the system catches that shadow medium.
Infotypes and policies decide the action
Teams define the infotypes, then policies that block, audit keywords, or audit files. Each match sends a violation.
A violation can become a risk incident
From the violation, the team opens a risk incident, so the blocked or audited event has an owner and a treatment path.
How it works
From an approved channel to a risk incident
Name the email, cloud drive, and AI tools the organisation allows, catch a shadow medium, and turn a policy violation into a risk incident.
Step 1
Approve the channels
Email, cloud drive, and AI models
Record the email service providers, cloud drive providers, and AI models the organisation allows. Everything the policies watch is measured against that list.
Includes
Platform features
What data loss prevention watches
Approved email providers
The email services the organisation allows, used as the boundary for outbound mail.
Approved cloud drives
The cloud drive providers the organisation allows, so files leave only through those drives.
Approved AI models
The AI models the organisation allows, public or private, named before anyone can use them.
Shadow mediums
An email service, cloud drive, or AI model outside the approved list is caught when someone uses it.
Infotypes
The data types a policy looks for in keywords and in files, defined by the organisation.
Block, audit, and warn
A policy blocks the action, audits the keywords, audits the file, or warns, and records which it did.
Violations sent
Each match is sent with the tool, the time, and the outcome, for the team that owns the channel.
Risk incident
A violation converts into a risk incident, with the channel, the infotype, and the policy on the record.
Outcomes
A shadow medium becomes a record the team can work
The approved list is the boundary
Email providers, cloud drives, and AI models the organisation allows are named in one place.
Shadow use is caught
A medium outside that list shows up when someone uses it, including a tool that had gone quiet.
A violation can be worked as a risk
Block, audit, and warn each send a violation, and that violation can be opened as a risk incident.
Platform capabilities
Approved channels, policies, and incidents
The organisation defines the infotypes and the policies. A match can block, audit keywords, or audit files, and the violation it sends can be opened as a risk incident.
- Approved email service providers, cloud drive providers, and AI models
- Shadow mediums caught when someone uses a channel outside that list
- Infotypes defined by the organisation for keywords and for files
- Policies that block, audit keywords, audit files, or warn
- A violation sent with the tool, the time, and the outcome
- A violation converted into a risk incident
- Dormant tools kept visible beside the channels still in use
Prevention scope
3
Approved channel types
Catch
Shadow mediums
Policy
Block or audit
Incident
From a violation
See the channel before the data leaves
Approve the email, cloud drive, and AI tools, catch shadow mediums, and convert a violation into a risk incident.
Frequently asked questions
Which channels does the organisation approve first?
The organisation lists the email service providers, cloud drive providers, and AI models that are allowed. Policies and shadow detection are measured against that list.
What happens when someone uses a shadow medium?
A shadow medium is an email service, cloud drive, or AI model outside the approved list. When someone uses it, the system catches that use, including a tool that had gone dormant.
How does a violation become a risk incident?
Infotypes and policies decide whether a match is blocked, audited, or warned. The violation is sent with the tool, the time, and the outcome, and the team can convert that violation into a risk incident.
Related products
Cyber Risk Management
Live risk scoring, control mapping, FAIR quantification, and smart remediation.
AI Data Monitoring
Monitor, audit, and block prompts and file uploads so sensitive data stays inside the organization.
Data Privacy & Protection
PII detection, sensitive data scanning, secret discovery, NER identification, and exposure scoring.
Observeri
AI agent
Welcome to Observeri - My Name is Misha, How may i help you today!
Your privacy choices
We use essential storage to remember your choices. With your permission, we also use analytics to understand website usage and marketing technologies to measure advertising, plus YouTube to show product videos. Optional tracking stays off until you choose. Read our Privacy Policy.