Third Party Risk Management
Your vendors. Their exposure. Your problem.
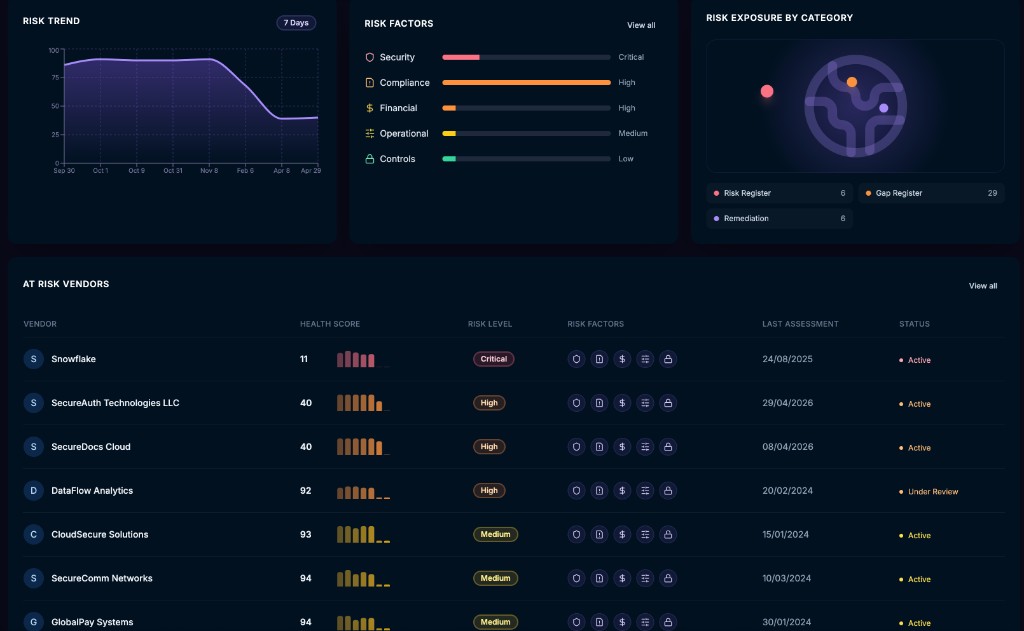
Observeri GRC autonomously maintains a live inventory and risk profile for every vendor, so you can answer one question anytime: are we safe to depend on them right now?
24/7
Continuous monitoring
AI
Risk prioritization
100%
Evidence-backed closure
Why it matters
Periodic reviews can't track constant vendor change
Vendor exposure changes constantly: new tools get adopted, access expands, and suppliers change their security posture. If you only review on a schedule, risk accumulates quietly until it shows up as an urgent scramble—or a breach.
Shadow vendors discovered only during audits or incidents
Questionnaires that go stale the moment they're submitted
No clear ownership when supplier risk shifts mid-contract
Remediation tracked in email threads without verified proof
What it is
Third party trust, continuously verified
Observeri Third Party Risk keeps vendor posture up to date autonomously. It finds vendors as they show up, assigns a risk tier with AI-assisted scoring, and keeps checking for changes. When something shifts, it starts the right review and tracks it until closure—with evidence.
Always-on discovery
Live posture scoring
Automated guardrails
How it works
Discover. Assess. Act. Close. Repeat.
A closed loop that refreshes vendor posture from live signals, recalculates risk when things change, and triggers the right next steps autonomously.
Step 1
Discover
Spot vendors the moment they appear
Observeri ingests vendor signals from onboarding workflows, asset inventory, SSO integrations, and manual intake—building a living vendor register aligned to what is actually in use, with ownership and business context attached.
Key signals
Risks we address
The vendor risks that accumulate when TPRM runs on spreadsheets.
Shadow vendor adoption
Teams onboard SaaS tools without security review, expanding your attack surface invisibly.
Impact: Unmonitored data flows and unassessed suppliers bypass your control framework.
Supplier data breach
A compromised vendor becomes the entry point to your customer data, IP, or credentials.
Impact: Regulatory fines, contractual liability, and reputational damage scale with data sensitivity.
Compliance & contractual gaps
DPAs, SOC 2 reports, and ISO attestations expire without triggering reassessment.
Impact: Audit findings and customer security questionnaires expose stale vendor evidence.
Fourth-party concentration
Critical vendors depend on sub-processors you never assessed or inventoried.
Impact: Supply chain blind spots create single points of failure across your ecosystem.
Access creep & privilege drift
Vendor accounts accumulate permissions beyond what the original engagement required.
Impact: Over-privileged third-party access becomes a persistent insider-threat vector.
Remediation without proof
Vendor gaps are marked closed in spreadsheets without verified corrective evidence.
Impact: Leadership and auditors cannot defend closure decisions during scrutiny.
Benefits
Always current risk. Always clear next steps.
Keep your vendor inventory accurate
Autonomously align your vendor list to what is actually in use, with ownership, tier classification, and service dependency context attached to every record.
Focus effort where it matters
AI risk prioritization ranks suppliers by real exposure—data touched, access level, business criticality—so review depth matches actual consequence.
Faster reviews with consistent decisions
Standardize what gets reviewed and who signs off. Low-risk vendors move quickly; higher-risk suppliers get the right depth without reinventing the process each time.
Close issues with verified completion
Track remediation to completion with automated evidence collection. Closures are confirmed, defensible, and easy to stand behind in audits and customer diligence.
Platform capabilities
Everything you need for enterprise-grade TPRM.
- Vendor onboarding with tiered risk classification and business owner assignment
- Contract and SLA management with renewal tracking and obligation mapping
- Questionnaire-based and automated vendor security assessments
- AI-assisted risk scoring with FAIR-aligned exposure quantification
- Continuous monitoring with posture change alerts and reassessment triggers
- Gap remediation workflows with SLA tracking and verified evidence closure
- Fourth-party and sub-processor dependency mapping
- Audit-ready vendor dossiers linked to compliance frameworks (SOC 2, ISO 27001, GDPR, DORA)
Quantified outcomes
60%
Less manual TPRM effort
3x
Faster vendor reviews
100%
Evidence-linked closures
24/7
Posture monitoring
Observeri advantage
Third Party Risk connects directly to Observeri's AI Risk Operations Center, Compliance Management, and Focused Remediation modules—so vendor findings flow into enterprise risk registers, control assessments, and executive dashboards without duplicate data entry.
Know your vendor exposure. Anytime.
Observeri Third Party Risk keeps discovery, reassessment, and closure running continuously—so you always know what changed, what matters, and what is verified.