External Attack Surface Management
Know every edge of your exposure — before attackers do.
Observeri EASM continuously discovers, scans, and prioritizes every public-facing asset across your digital footprint—domains, subdomains, cloud services, open ports, shadow IT, and dark-web signals—so GRC and security teams close exposure with evidence, not guesswork.
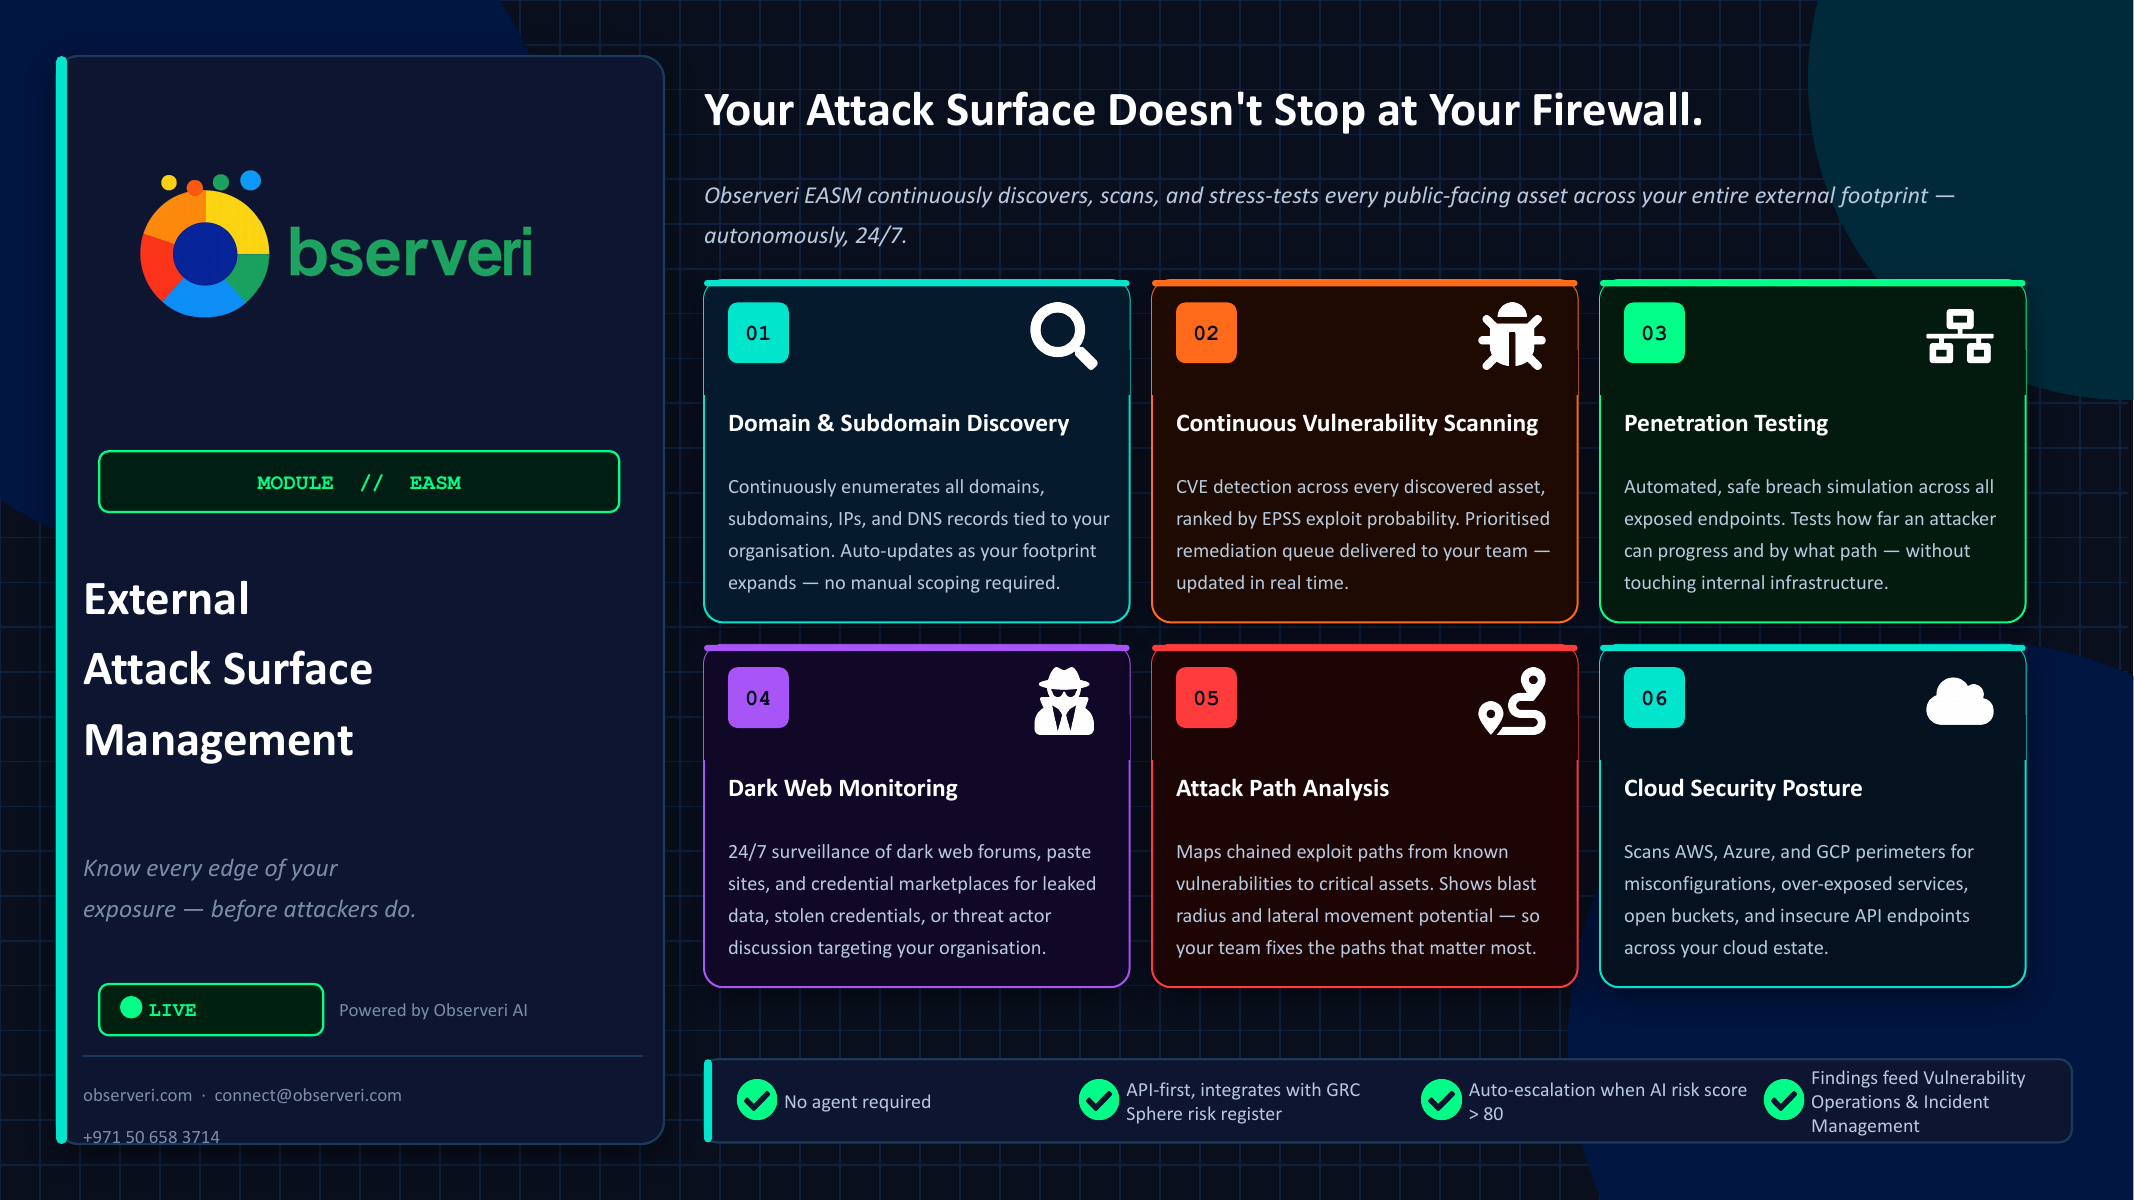
24/7
External discovery
AI
Risk prioritization
GRC
Linked remediation
Product preview
See External Attack Surface Management in action
A short tour of hosts, ports, intelligence, shadow IT, attack paths, web pentest, smart contracts, and cloud posture—hostname text is blurred to protect customer anonymity.
Analytics dashboard
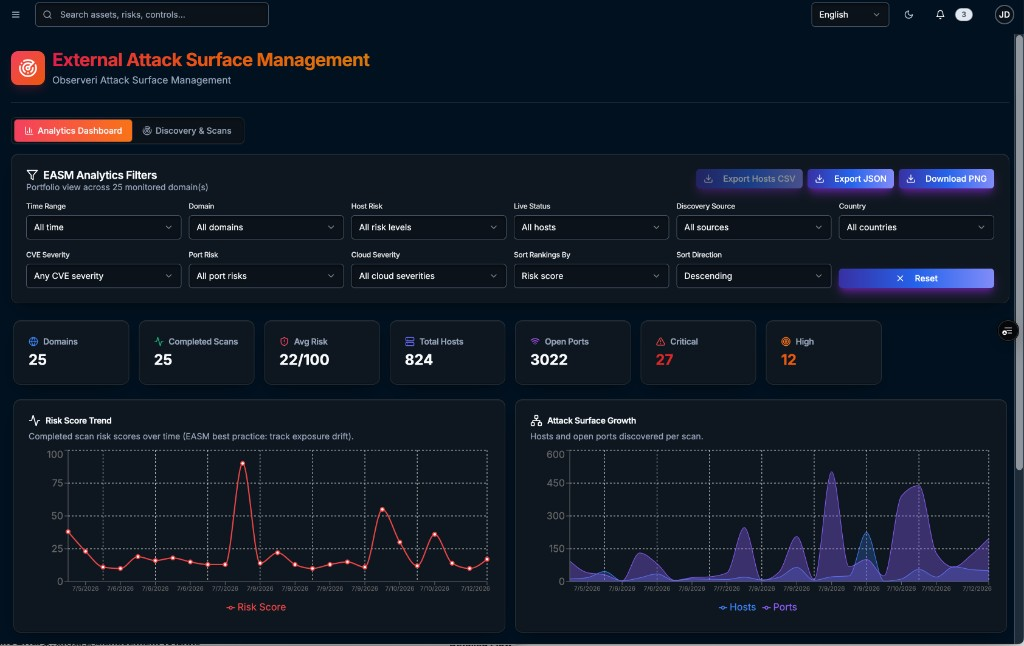
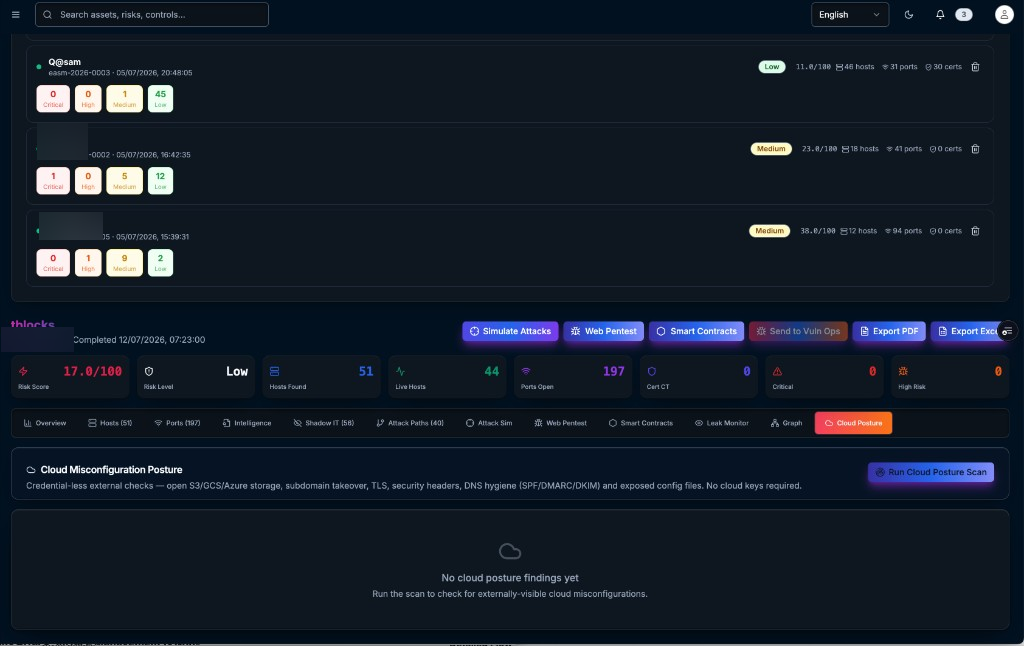
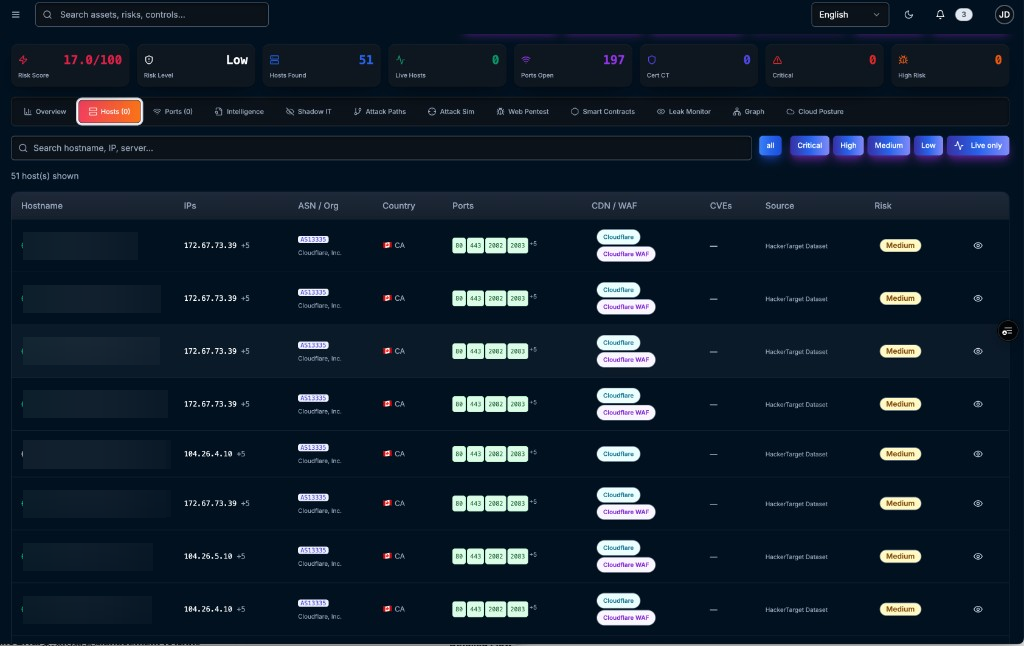
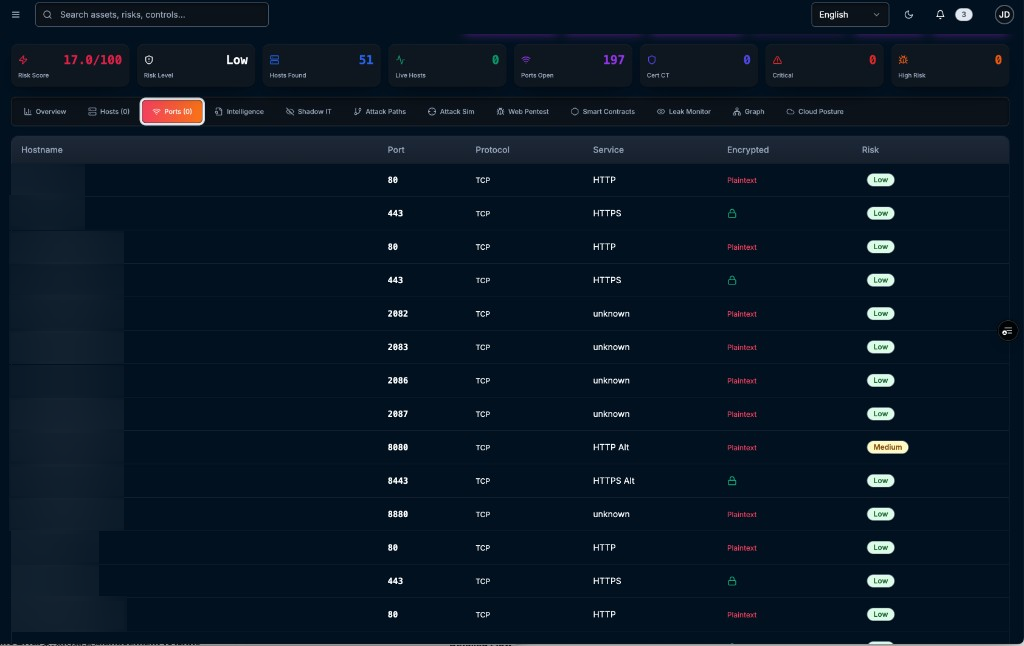
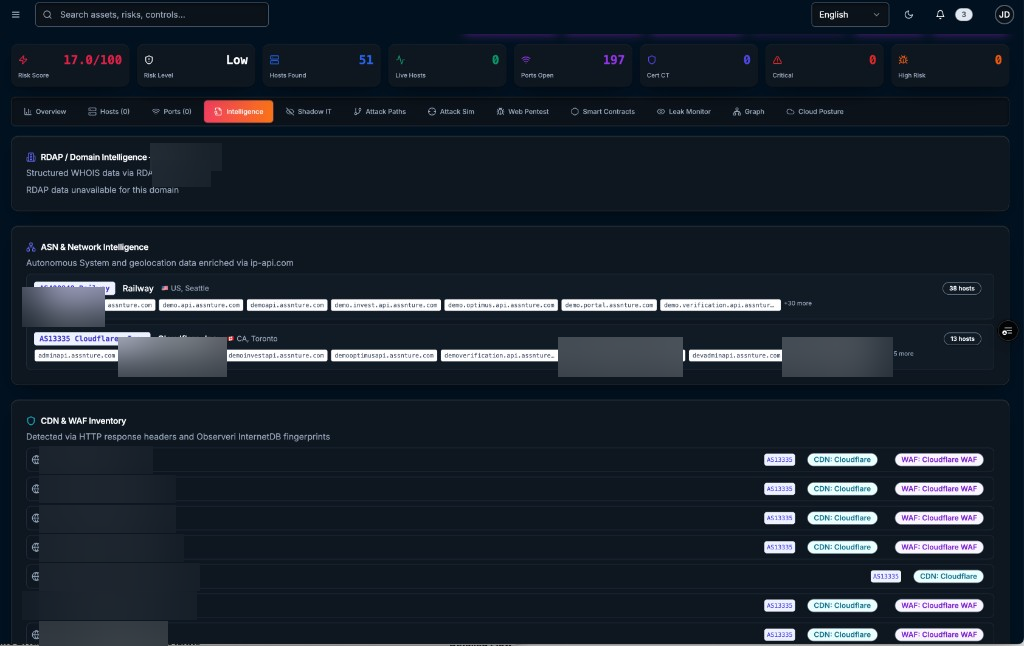
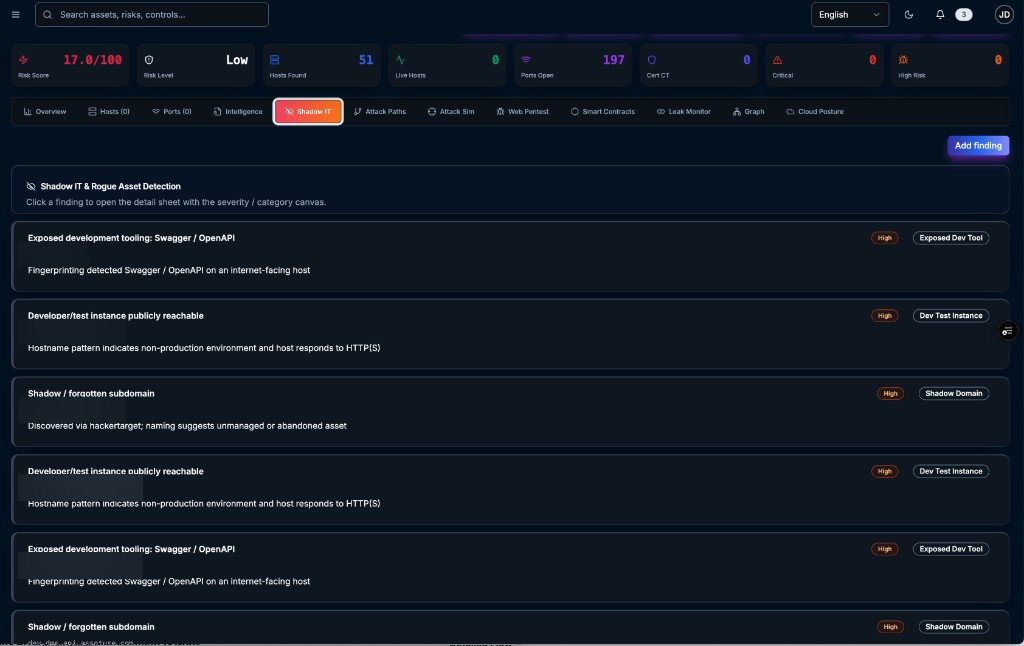
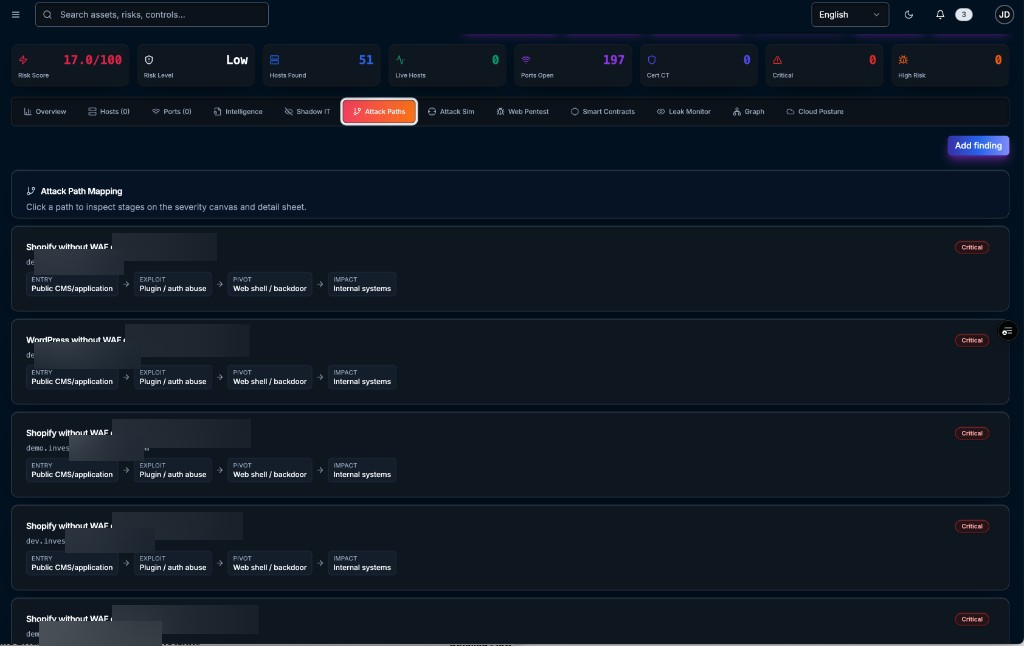
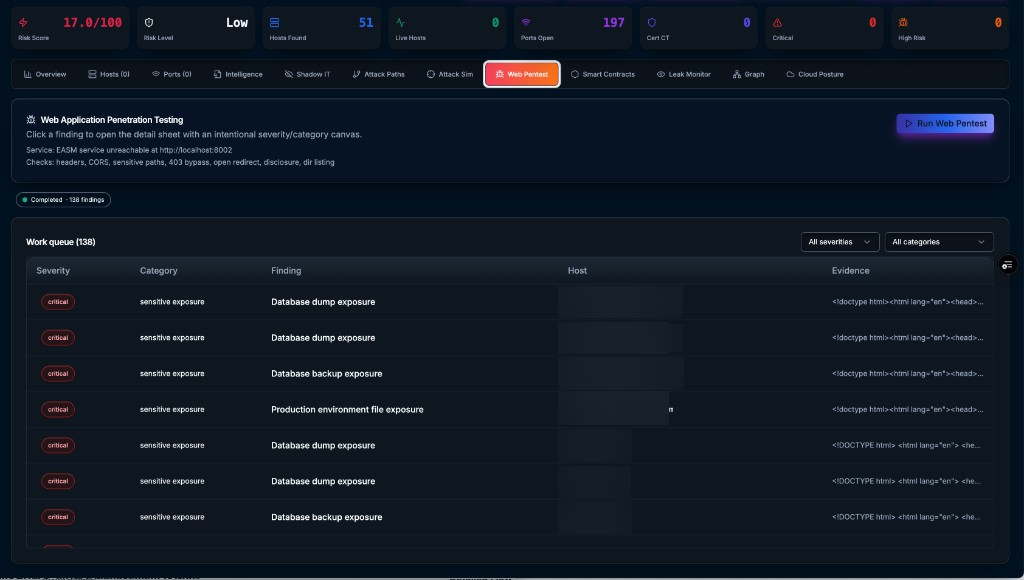
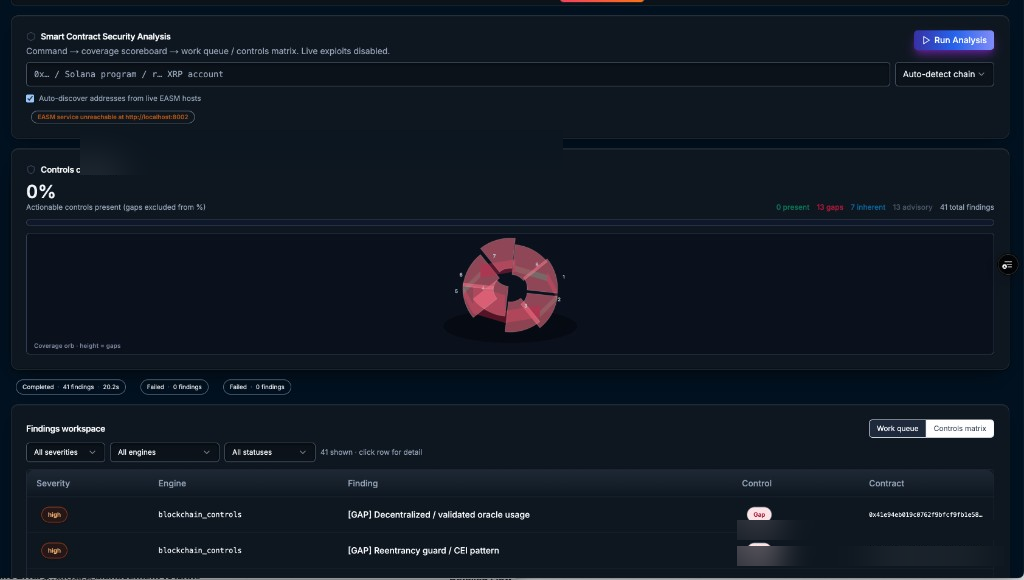
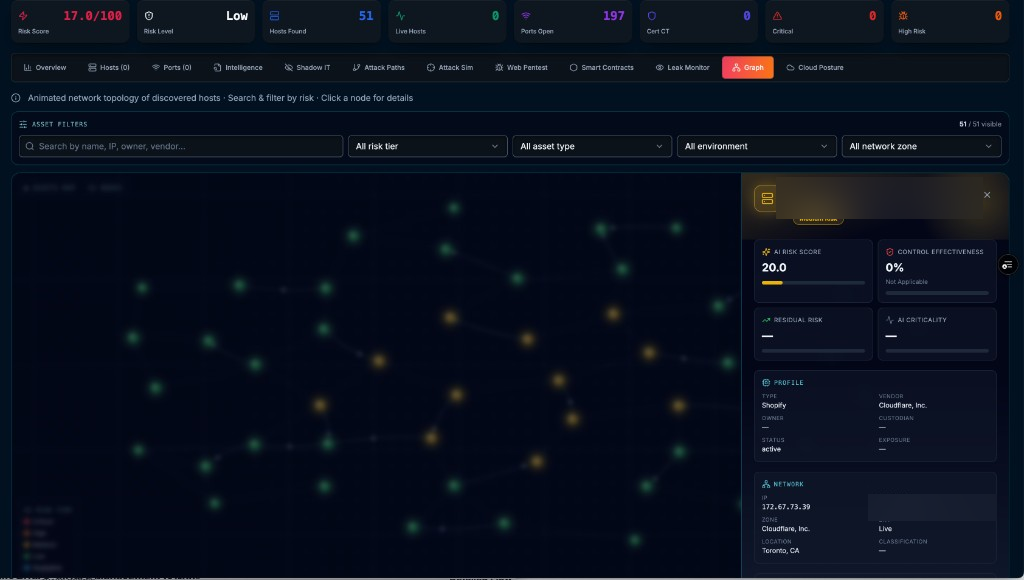
Hostnames and identifying asset labels are anonymized in these previews.
Why it matters
Your attack surface doesn't stop at the firewall
Unknown internet-facing assets
Forgotten subdomains, shadow cloud instances, and unsanctioned SaaS expand faster than inventories can track—creating blind spots attackers find first.
Fragmented external scanning
Port scans, cert transparency, and one-off pentests live in different tools with no shared risk score or path to GRC remediation ownership.
Shadow IT goes unmanaged
Dev/test instances, exposed Swagger endpoints, and abandoned CMS installs remain reachable without WAF, ownership, or SLA.
No bridge to GRC workflows
External findings rarely update the risk register, vulnerability operations queue, or board-level exposure metrics in time to matter.
What it is
Continuous external attack surface management for Observeri GRC
EASM is Observeri's outside-in visibility layer. It enumerates your public footprint, enriches assets with ASN/CDN/WAF intelligence, detects shadow IT, maps attack paths, runs web and smart-contract checks, and feeds prioritized findings into Vulnerability Operations and the AI Risk Operations Center.
Domain & subdomain discovery
Continuously enumerate domains, subdomains, IPs, and DNS records tied to your organization—auto-updating as the footprint expands.
Hosts, ports & services
Inventory live and historical hosts with open ports, protocols, encryption status, and risk badges for plaintext exposures.
Intelligence enrichment
Enrich assets with ASN, CDN, WAF, geolocation, and RDAP context so teams know who hosts what—and where exposure concentrates.
Shadow IT detection
Flag rogue subdomains, public dev/test instances, and exposed developer tooling such as Swagger/OpenAPI on internet-facing hosts.
Attack path analysis
Map chained exploit paths from public entry points through pivot stages to business impact—so teams fix the routes that matter most.
Web pentest & cloud posture
Run credential-less external checks for sensitive paths, misconfigurations, TLS/DNS hygiene, and exposed cloud storage without cloud keys.
Discover continuously
Prioritize with AI
Remediate in GRC
How it works
Discover. Enrich. Expose. Prioritize. Remediate.
A continuous outside-in loop—from external discovery through AI prioritization and GRC-linked closure.
Step 1
Discover
Map the external footprint
Seed domains and continuously discover hosts, certificates, ports, technologies, and cloud-facing services across your digital estate.
Activities
Platform features
Built for continuous external exposure reduction
Analytics dashboard
Track domains monitored, completed scans, average risk, host growth, open ports, and critical/high counts across your EASM programme.
Asset graph
Explore an animated network topology of discovered hosts, filter by risk tier, and inspect AI risk and control effectiveness per asset.
Smart contract analysis
Analyze blockchain program addresses discovered from live EASM hosts, with controls coverage and a findings work queue for gaps.
Export & integration
Export hosts and findings, simulate attacks, and escalate into Vulnerability Operations without leaving the Observeri GRC workflow.
Benefits for your organization
Turn external discovery into governed remediation
Eliminate external blind spots
Replace static inventories with continuous discovery so new subdomains, ports, and cloud exposures appear in the programme—not in an incident ticket.
Prioritize the real attack paths
Move beyond raw CVE lists to path-aware and severity-aware queues that show how an attacker can progress from a public CMS to internal impact.
Govern external risk like internal risk
Feed EASM findings into the same GRC spine used for vulnerabilities, assets, and board reporting—so external exposure has owners and SLAs.
Prove reduction over time
Use risk-score trends and attack-surface growth charts to show whether discovery is expanding faster than remediation—or the other way around.
For CISOs
A live view of internet-facing risk, shadow IT, and critical external findings tied to enterprise risk reduction—not tool sprawl.
For security operations
One work queue for hosts, ports, pentest findings, attack paths, and cloud posture with evidence ready for remediation handoff.
For GRC & compliance
External exposure becomes auditable: discovered assets, prioritized issues, and closure evidence linked to Observeri GRC controls.
Platform capabilities
Enterprise EASM, connected to Observeri GRC
- Continuous domain, subdomain, host, and port discovery
- ASN, CDN, WAF, and geographic intelligence enrichment
- Shadow IT and rogue asset detection
- Attack path mapping from entry to impact
- Web application penetration testing work queues
- Smart contract security analysis with controls coverage
- Credential-less cloud misconfiguration posture checks
- Analytics for risk trends and attack-surface growth
- Asset graph with per-host AI risk scores
- Escalation into Vulnerability Operations and the risk register
Quantified outcomes
24/7
Continuous discovery
Outside-in
No agent required
AI
Risk prioritization
GRC
Linked remediation
Connected to Observeri GRC
EASM integrates with Exposure Management, Vulnerability Operations, and the AI Risk Operations Center—so every external finding can update asset risk scores and drive governed remediation.
Illuminate your external footprint before attackers do
Continuously discover internet-facing assets, prioritize real attack paths, and close exposure inside the same GRC programme your board already trusts.